

Vulnerability Scanning Products
VANS Vulnerability Reporting Assistant ToolDVM Vulnerability Scanner (Full Chinese Interface)Downloads
Product CatalogVulnerability Scanning Products
VANS Vulnerability Reporting Assistant ToolDVM Vulnerability Scanner (Full Chinese Interface)Downloads
Product CatalogSeptember 23, 2026
When major vulnerabilities are disclosed but not identified and patched in time, government agencies and businesses can face disrupted operations and even reputational damage. The Vulnerability Analysis and Notice System (VANS) helps government agencies and enterprises see the weaknesses in their own systems. Think of a typhoon on the way: you would want to know exactly which parts of your neighborhood and home need reinforcing. VANS works like a patrol officer, rapidly checking against a vulnerability database, flagging known risks, and offering remediation advice. Through the reporting platform it automatically matches software assets against known vulnerabilities, performs software asset inventory (CPE), and tracks potential vulnerabilities (CVE) — so when a security incident occurs, you can respond immediately and keep the damage to a minimum.
Promulgated on November 21, 2018, the ‘Regulations on the Classification of Cybersecurity Responsibility Levels’ require Tier A, B, and C government agencies and critical infrastructure providers to implement a cybersecurity vulnerability reporting mechanism.
| Cybersecurity Responsibility Level | Requirements |
|---|---|
| Tier A & B Government Agencies | 1. Must complete implementation of the vulnerability reporting mechanism within one year of initial designation or level change, maintain ongoing operations, and submit information asset inventory data in the format specified by the competent authority. 2. Agencies designated before the amendment took effect on August 23, 2021 must complete implementation within one year of the amendment's effective date, maintain ongoing operations, and submit information asset inventory data as specified. |
| Tier A & B Specific Non-Government Entities | 1. Critical infrastructure providers must complete implementation of the vulnerability reporting mechanism within one year of initial designation or level change, maintain ongoing operations, and submit information asset inventory data in the format specified by the competent authority. 2. Providers designated before the amendment took effect on August 23, 2021 must complete implementation within one year of the amendment's effective date, maintain ongoing operations, and submit information asset inventory data as specified. |
| Tier C Government Agencies | 1. Must complete implementation of the vulnerability reporting mechanism within two years of initial designation or level change, maintain ongoing operations, and submit information asset inventory data in the format specified by the competent authority. 2. Agencies designated before the amendment took effect on August 23, 2021 must complete implementation within two years of the amendment's effective date, maintain ongoing operations, and submit information asset inventory data as specified. |
| Tier C Specific Non-Government Entities | 1. Critical infrastructure providers must complete implementation of the vulnerability reporting mechanism within two years of initial designation or level change, maintain ongoing operations, and submit information asset inventory data in the format specified by the competent authority. 2. Providers designated before the amendment took effect on August 23, 2021 must complete implementation within two years of the amendment's effective date, maintain ongoing operations, and submit information asset inventory data as specified. |
Further reading: Cybersecurity Guidelines for Listed Companies
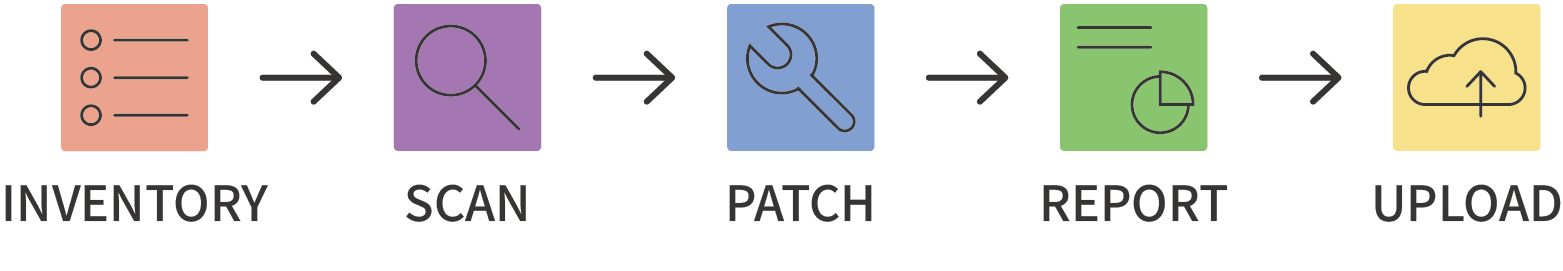
Beyond asset inventory and vulnerability patching, additional modules are available, including GCB/FCB Government and Financial Security Configuration Audit Software, which helps government, financial, and enterprise IT equipment follow a standardized set of security configurations, and complements ISO 27001/27002 (Section 8.9 Configuration Management) requirements by providing a management tool for establishing security configuration standards for hardware, software, services, and networks.
What we offer isn't a single tool, but a comprehensive security management platform that supports cross-platform integration across Windows, Linux, Mac, AIX, and more — giving administrators easy control and ensuring uninterrupted security management.