

Vulnerability Scanning Products
VANS Vulnerability Reporting Assistant ToolDVM Vulnerability Scanner (Full Chinese Interface)Downloads
Product CatalogVulnerability Scanning Products
VANS Vulnerability Reporting Assistant ToolDVM Vulnerability Scanner (Full Chinese Interface)Downloads
Product Catalog
Comprehensive security compliance inventory and management starts with knowing your assets.
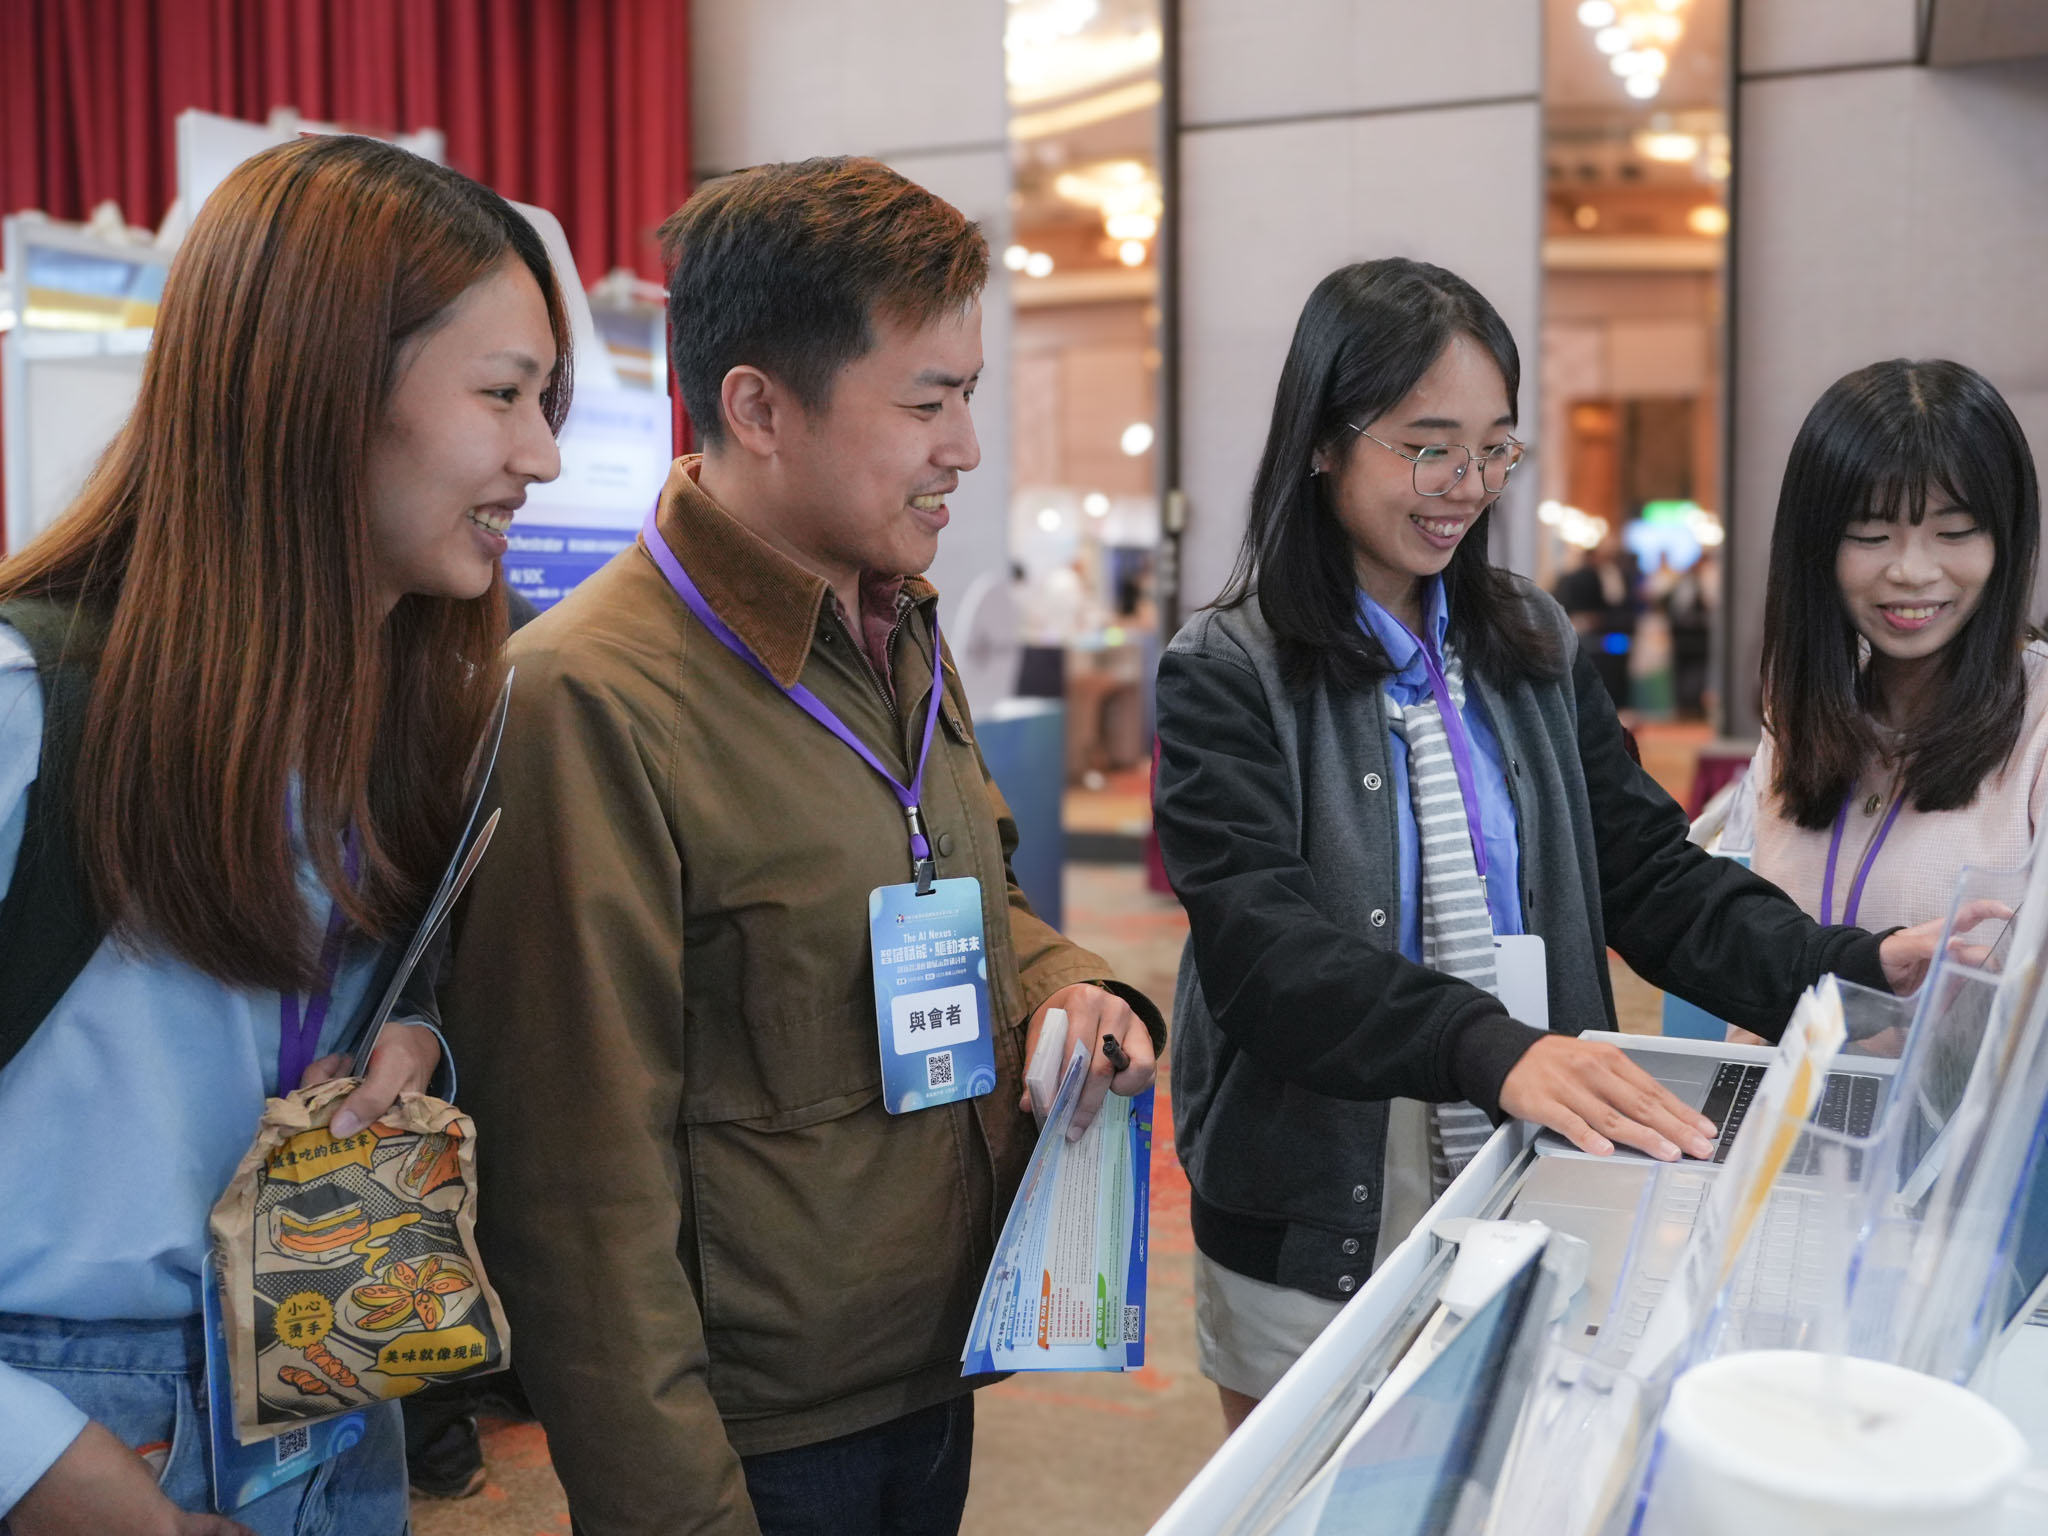
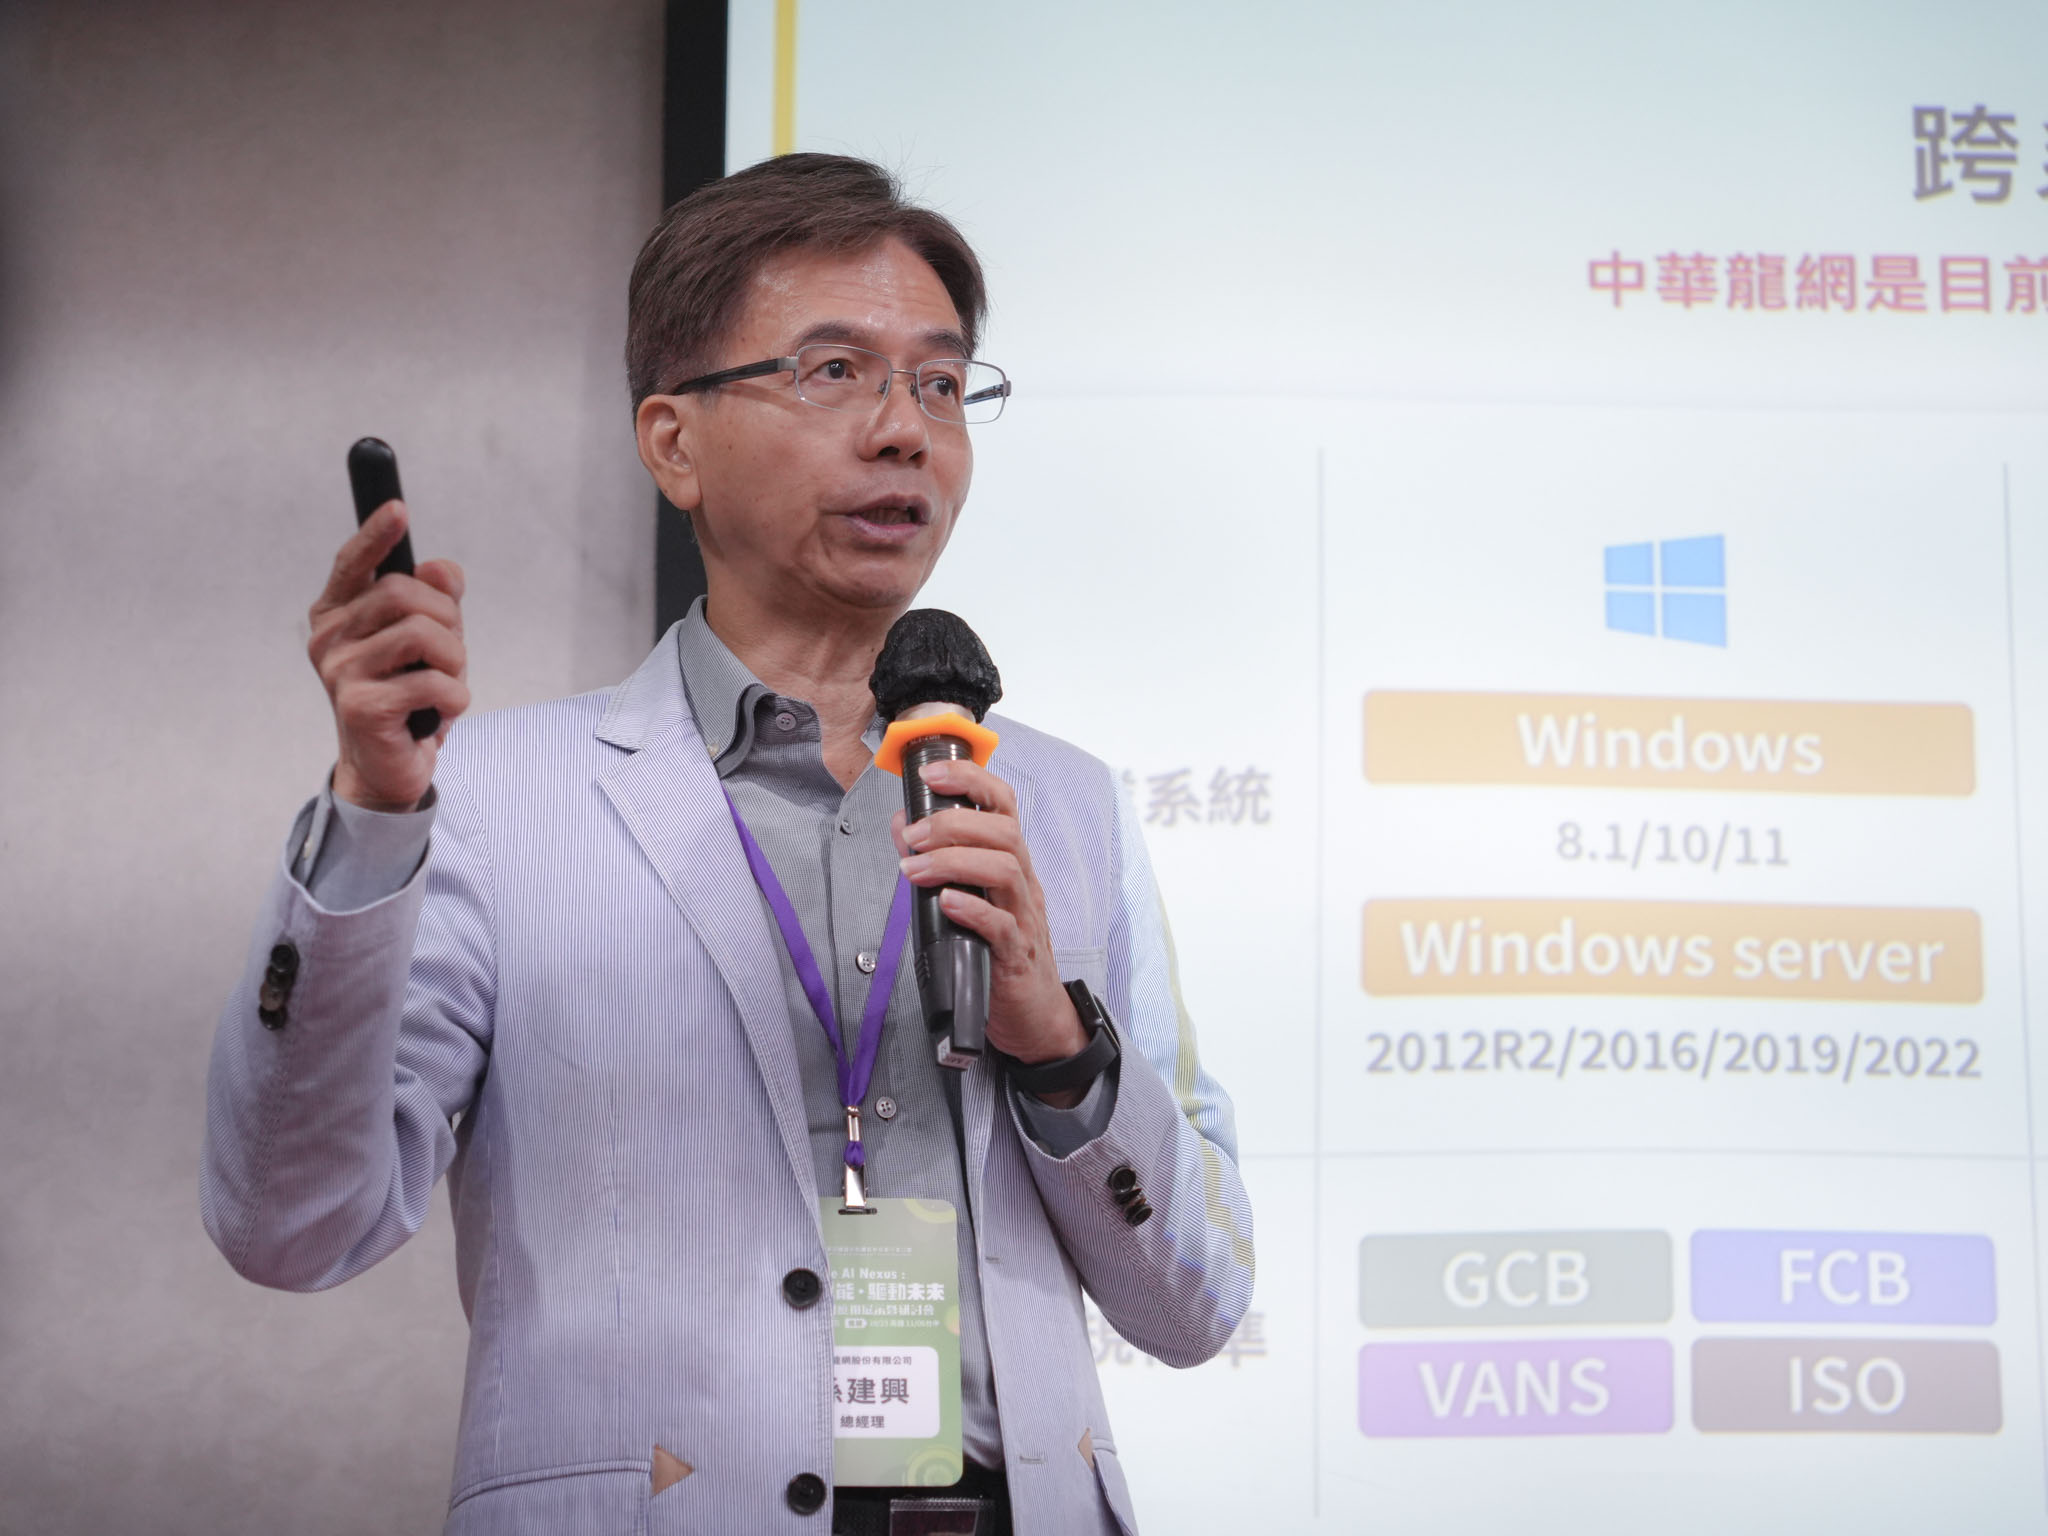
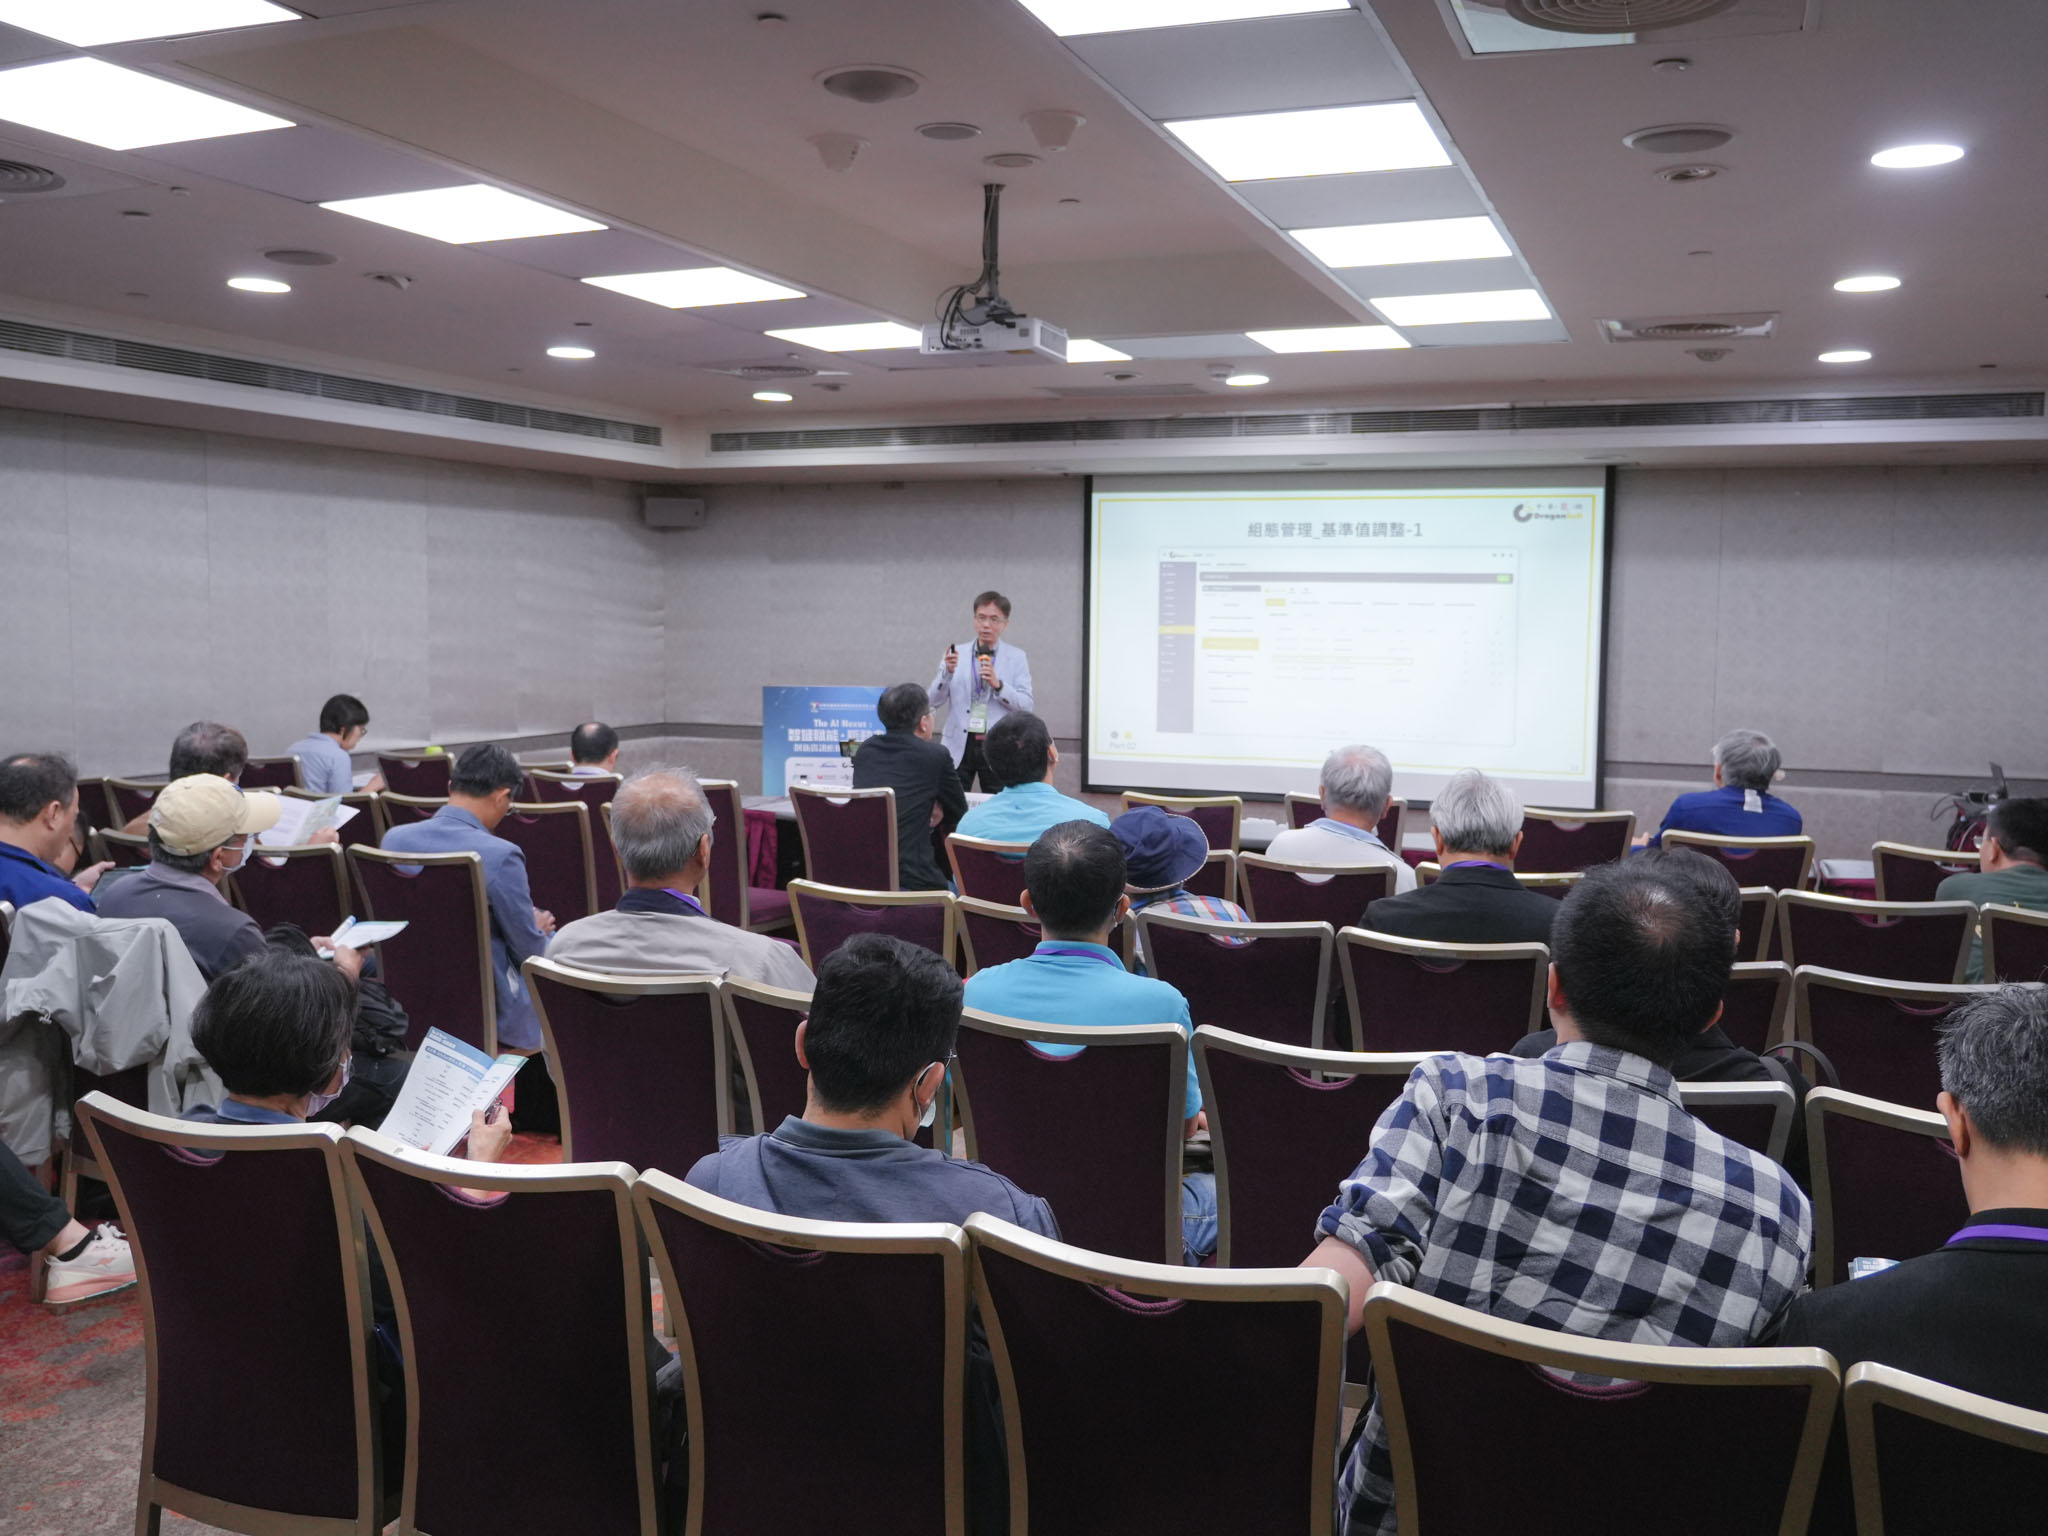
Organized by the Information Service Industry Association of R.O.C. (CISA), the 2026 Innovative IT Applications Exhibition and Seminar was held on October 30 at the NTUH International Convention Center in Taipei. Under the theme “The AI Nexus: Intelligent Chains Empowering the Future,” the event brought together IT solutions spanning AI applications, cloud security, smart governance, and other innovative fields.
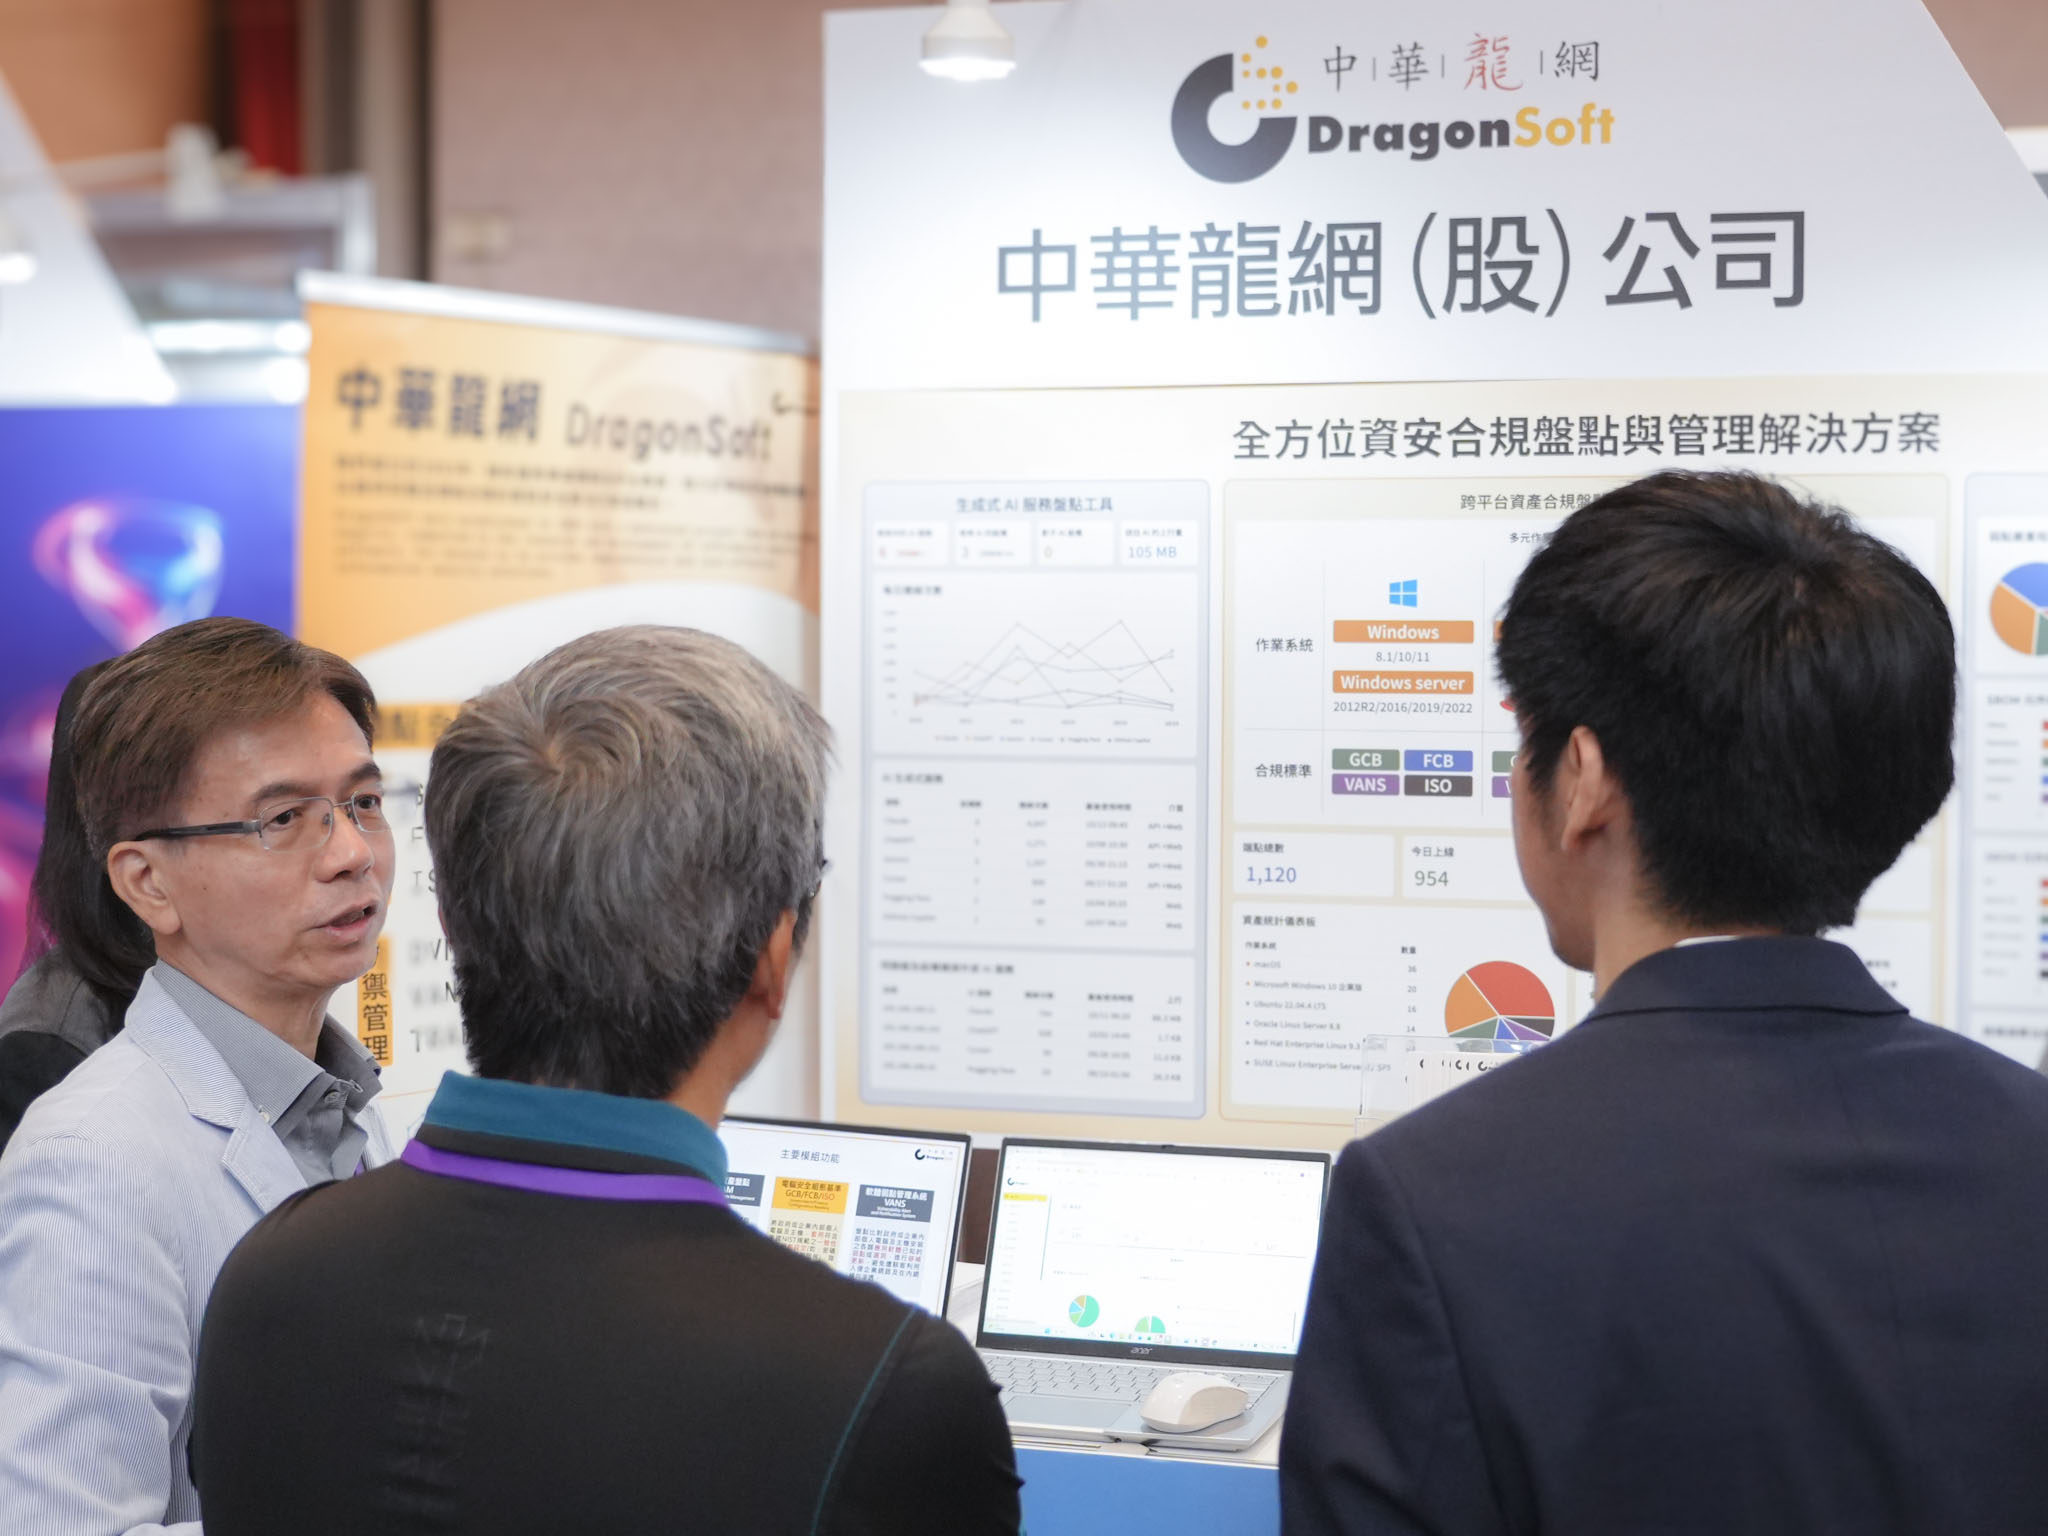
DragonSoft exhibited its Comprehensive Security Compliance Inventory and Management Solution, using live demonstrations and conversations to show how enterprises and government agencies can gain visibility into IT assets, configuration compliance, and software security risks from multiple angles.
In IT environments where multiple operating systems coexist, integrated management of asset inventories, configuration settings, and compliance status is a foundation of organizational security governance.
DragonSoft’s cross-platform asset compliance inventory and management platform supports Windows, Linux, macOS, AIX, and more. It helps administrators track device assets and configuration status, and improves the efficiency of asset management and audits through compliance checks and visual reporting.
As generative AI tools become part of everyday work, organizations need clearer visibility into how AI services are used internally.
Generative AI service inventory lets administrators review AI service usage along with device and connection records, helping them identify related applications and potential risks and establish a clearer basis for managing AI service use.
Software security management requires knowing not only which applications are installed, but also the components and dependencies used inside them.
With a Software Bill of Materials (SBOM), organizations can understand component types, vulnerability severity, license information, and component health, providing a reference for subsequent vulnerability assessment and software supply chain risk management.
Through demonstrations and on-site discussions, attendees learned more about how cross-platform asset management, generative AI service inventory, and SBOM software composition analysis can be applied.
From devices to software, and from configuration settings to AI services, gaining full visibility into what needs to be managed—and the risks involved—is an essential step toward effective security governance.